AI Regulatory Compliance Obligations for Enterprise Legal Departments
Legal departments must coordinate AI compliance across three overlapping regulatory regimes.
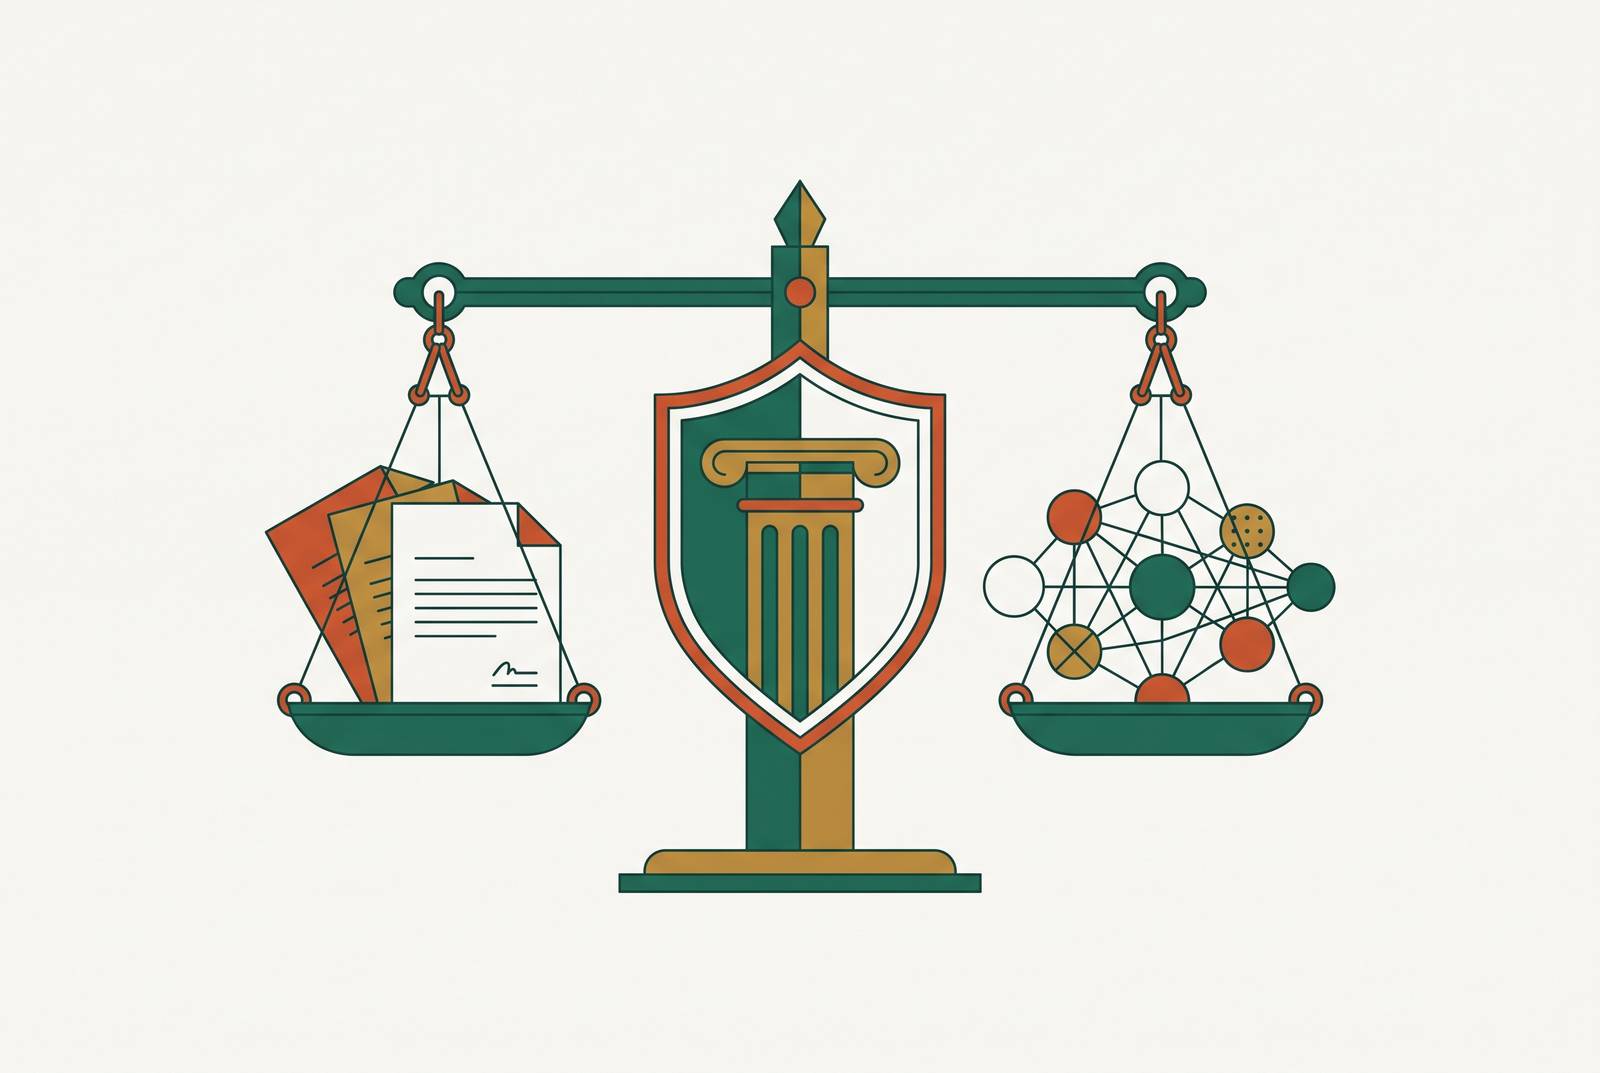
Enterprise legal departments must meet AI obligations that overlap under professional conduct rules, data protection statutes, and the EU AI Act. A defensible compliance program must connect those obligations to named owners throughout the system’s lifecycle. Legal operations is best positioned to coordinate that program, while individual lawyers remain responsible for the professional duties no institutional policy can discharge for them.
Why enterprise legal teams now face three simultaneous and enforceable compliance regimes
The EU AI Act’s prohibited-practice provisions began to apply on 2 February 2025, and its general-purpose AI model obligations began to apply in August 2025. Professional conduct rules and data protection statutes predate generative AI but already apply to its use. These regimes operate in parallel, reaching the lawyer, the personal data processed, and the AI system itself. Only one is AI-specific legislation.
The US adds an uneven state-law patchwork. Texas TRAIGA took effect January 1, 2026, while Colorado’s AI Act, now replaced by SB 26-189, is scheduled for January 1, 2027. Utah’s disclosure requirements are already in force, and California’s health-care-adjacent provisions have a staged rollout. The practical response is to build around the strictest applicable state requirements. That work is already behind adoption, as individual lawyers’ use of generative AI has surged while a substantial share of legal departments have neither a formal AI policy nor plans to create one.
How ownership of these three regimes stays unsettled inside most legal departments
Awareness does not resolve the allocation of responsibility. Individual lawyers have conduct duties, while privacy and security teams usually handle data protection outside legal’s direct control. The AI system itself may have no named owner or documented review protocol until a client questionnaire or regulatory inquiry demands one. Each function can address its own remit while leaving the overall deployment ungoverned. Procurement and retained records are particularly exposed when programs concentrate on deployment and daily operation.
Agentic AI makes this gap more consequential. Agents can execute code, sign contracts, and book transactions, but no definitive rulings have allocated liability between users and developers for autonomous errors. Vendor indemnification needs to be checked to see whether it expressly covers autonomous actions and hallucinations that lead to financial loss. Meanwhile, courts hold lawyers responsible for AI-generated errors regardless of who selected the tool or what the vendor promised. A department that delegates tool selection to IT and policy drafting to legal ops can retain exposure without having controlled the decisions that created it. Legal must take a role in governance before anyone assigns it one.
What professional conduct rules actually require when a lawyer deploys AI
ABA Formal Opinion 512 applied existing technical-competence duties under Rule 1.1 to generative AI. It did not create those duties anew. A lawyer needs a reasonable understanding of the specific tool’s capabilities and limitations, and must independently verify its output to a degree appropriate to the tool and task. Hallucination is therefore both a product defect and a professional responsibility issue. In cases involving AI-generated errors, courts have imposed sanctions that range from warnings to six-figure monetary penalties and bar suspensions.
Confidentiality makes vendor handling of information a professional responsibility question. Rule 1.6 protects information about client representation, while Rules 1.9(c) and 1.18(b) also protect information about former and prospective clients. Privilege requires a separate analysis before vendor selection because voluntary disclosure to a third-party AI vendor can waive attorney-client privilege and work-product protection. Security review alone cannot settle that question. Rules 5.1 and 5.3 also require supervision of AI-generated work, with the review standard a supervising lawyer would apply to a junior associate’s draft.
The ABA Model Rule requires state adoption to serve as controlling text, and state ethics opinions govern where issued. Institutional approval does not displace that jurisdiction-specific analysis. Because competence, confidentiality, and supervision attach to lawyers, a governance policy cannot fully substitute for their understanding and judgment.
Where data protection statutes create obligations the conduct rules do not cover
A lawyer can meet professional duties while using a system that fails to meet privacy requirements. Data protection statutes independently regulate what personal data the system processes, how it is stored, and what the vendor does with it. Commercial contracts routinely contain named counterparties, authorized signatories, and contact details that can bring processing within GDPR and equivalent protections. Privacy compliance has its own enforcement authority. Italy’s €15 million fine against OpenAI for GDPR violations in training data processing shows the risk that remains after a professional-conduct review alone.
Data processing addenda, sub-processor lists, and retention schedules set out what the vendor agrees to do before the first document enters the system. Domestic requirements also apply to qualifying deployments without an EU nexus, including California’s staged provisions and Utah Code Ch. 13-77. Utah includes legal advice as a high-risk category requiring proactive disclosure by licensed professionals. These requirements cannot be inferred from compliance with confidentiality rules.
Documented review connects the two regimes without merging them. Evidence of what data entered the system, what it produced, and who reviewed the output supports both a privacy compliance demonstration and a response to a conduct complaint. Aspirational privacy statements are insufficient without documented controls and technical safeguards. The record must show that the specific obligation under review has been met.
What the EU AI Act requires from organizations using AI in high-risk legal workflows
The EU AI Act regulates the AI system as an object of law, adding conformity, documentation, and human oversight requirements. Prohibited practices applied from 2 February 2025, general-purpose AI model obligations from August 2025, and most of the Regulation applies from 2 August 2026. Earlier phases already require operational attention. Work on the remaining provisions must start before they all apply.
The Act also reaches beyond the model developer. Downstream organizations must verify that systems they deploy do not fall within prohibited categories and that general-purpose AI model vendors have published required training data summaries. For high-risk systems, conformity assessments, risk management systems, and operational human oversight form the compliance structure, with responsibility mapped to the organization’s role in the supply chain. These are ongoing requirements. Legal workflows need to be checked against the Act’s high-risk definitions to determine the status of each use of legal AI.
Procurement must check vendor compliance because a supplier that fails to comply creates risk for those using its products and could disrupt the supply chain. The financial stakes warrant board-level attention. Fines for the most serious violations reach tens of millions of euros or a percentage of global revenue.
Where the compliance obligation attaches across the AI system lifecycle — and who owns each stage
Procurement is where legal, privacy, and system obligations first converge. The vendor agreement must address privilege protection, data processing terms, sub-processor commitments, GPAI compliance verification, and relevant agent indemnification. Procurement or IT cannot answer those questions alone. Ownership at this stage must connect their purchasing role with legal and privacy review. A material change to the product calls for a fresh review, even when the vendor stays the same.
At Deployment, the team decides which uses and data types to approve. The approval scope should identify which legal work the system may support and match that scope against the Act’s high-risk definitions. This requires an accountable decision about permitted use. Without a documented boundary, an approval does not establish whether a later workflow was considered.
Operation places responsibility with those who produce and supervise the work. The program must identify who reviews output before it leaves the team and the standard applied. Rules 5.1 and 5.3 operate at this stage. Documenting human review provides evidence of supervision rather than merely an assertion that someone remained involved.
Record assigns responsibility for preserving that evidence. The questions are what is retained, for how long, and in what form. Regulators and opposing parties ask about this stage first, yet programs often leave it unassigned. Lifecycle ownership is incomplete if no one is responsible for demonstrating what happened after the underlying work closes.
The four operational controls that hold a compliance position across all three regimes
An inventory of every AI system establishes the program’s scope. It must include personal tools used by individual lawyers as well as institutionally approved deployments. Formal procurement does not define the conduct duty’s reach. Excluding shadow AI would leave the inventory narrower than the department’s actual exposure.
Naming an owner for each system makes clear who must answer for it. “Legal ops owns AI” identifies a function but not the person responsible for a regulatory inquiry. The designation must be specific to the deployment. Coordinating the program and owning a system are separate duties, even when the same function helps with both.
A documented human review step establishes the standard before deployment. It should state what the reviewer checks, the criteria applied, and what happens when output fails. Reconstruction after an error is not a substitute. The control must operate before output leaves the team.
Retained evidence establishes that the review actually occurred. Audit logs should survive the lifecycle of the legal work the system touched, with duration mapped to the longest applicable retention obligation across the three regimes. The durable policy anchor is the NIST AI Risk Management Framework. A framework-based program can absorb legislative change without requiring its basic governance structure to be rewritten each session.
Why legal operations is the function best positioned to own AI governance across all three regimes
Legal operations has the capabilities this program requires. Technology evaluation, workflow standardization, vendor management, metrics, and compliance monitoring map directly to the work of governing AI. Legal ops can coordinate a program across functions while leaving individual professional duties and specific system accountability intact. Its role is to connect responsibilities that otherwise remain separate.
Legal ops typically leads vendor selection, where privilege analysis, data processing agreement review, GPAI verification, and agent indemnification enter the same conversation. Greater GC involvement in technology sourcing, driven by exposure from AI errors, supports that mandate. Measurement gives the program a further strategic purpose. Most AI-using legal teams cannot formally measure whether their investment is working, while compliance logs, review records, and outcome tracking also support ROI assessment.
Teams that track AI value often measure quality and error reduction, how much outside-counsel spend they avoid, and how much they reduce internal labor costs. The governance infrastructure can support those measures without separating accountability from performance. A legal ops function that owns the program, measures outcomes, and reports them to the GC and board is operating as a strategic partner.
How contract intelligence fits into the governance program as both a governed system and a governance tool
Contract review is the legal department’s most AI-intensive workflow, making contract intelligence a concrete test of the governance program. These platforms process privileged documents and personal data while operating as AI systems subject to the Act’s applicable requirements. Vendor selection is therefore a legal decision before it is a purchasing decision. Threshold questions include whether customer contract data is used for training, which sub-processors are involved, and whether output can be verified against source text. Approved work types, documented review standards, and retained audit trails must then extend that analysis through deployment, operation, and record.
With proper governance, the platform can also help govern the rest of the portfolio. Obligation tracking, clause-level checks against playbook positions, and renewal and notice-date monitoring turn contract commitments into work that can be monitored. Obligation tracking and renewal alerting are among enterprise contract management’s highest-ROI applications. Their value depends on commitments being mapped.
The same principle applies to institutional knowledge. Each AI Act assessment, data processing agreement review, and state-law impact assessment done through the platform should be kept when the work closes and used to guide the next one. A named owner, documented review, and retained evidence make the platform both an accountable deployment and a means of demonstrating governance to regulators, auditors, and the board.